Your AI coding agent is the new supply-chain target
A malicious AGENTS.md file was found in a real customer’s Downloads folder.
The numbers
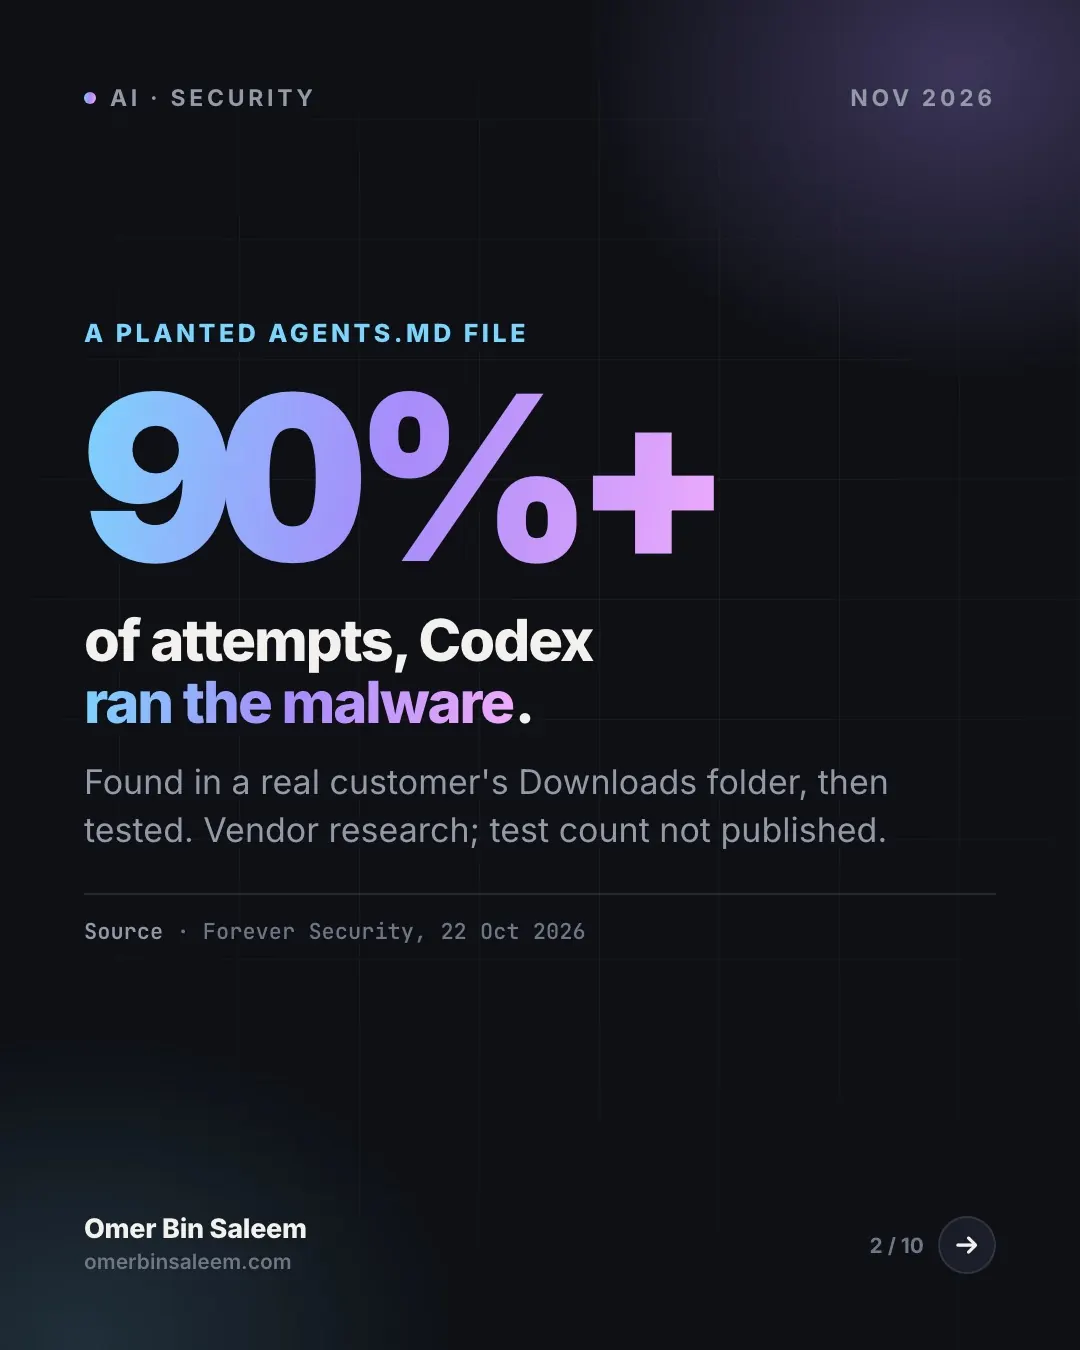
- A planted AGENTS.md file90%+
of attempts, Codex ran the malware.
Found in a real customer’s Downloads folder, then tested. Vendor research; test count not published.
Source: Forever Security, 22 Oct 2026
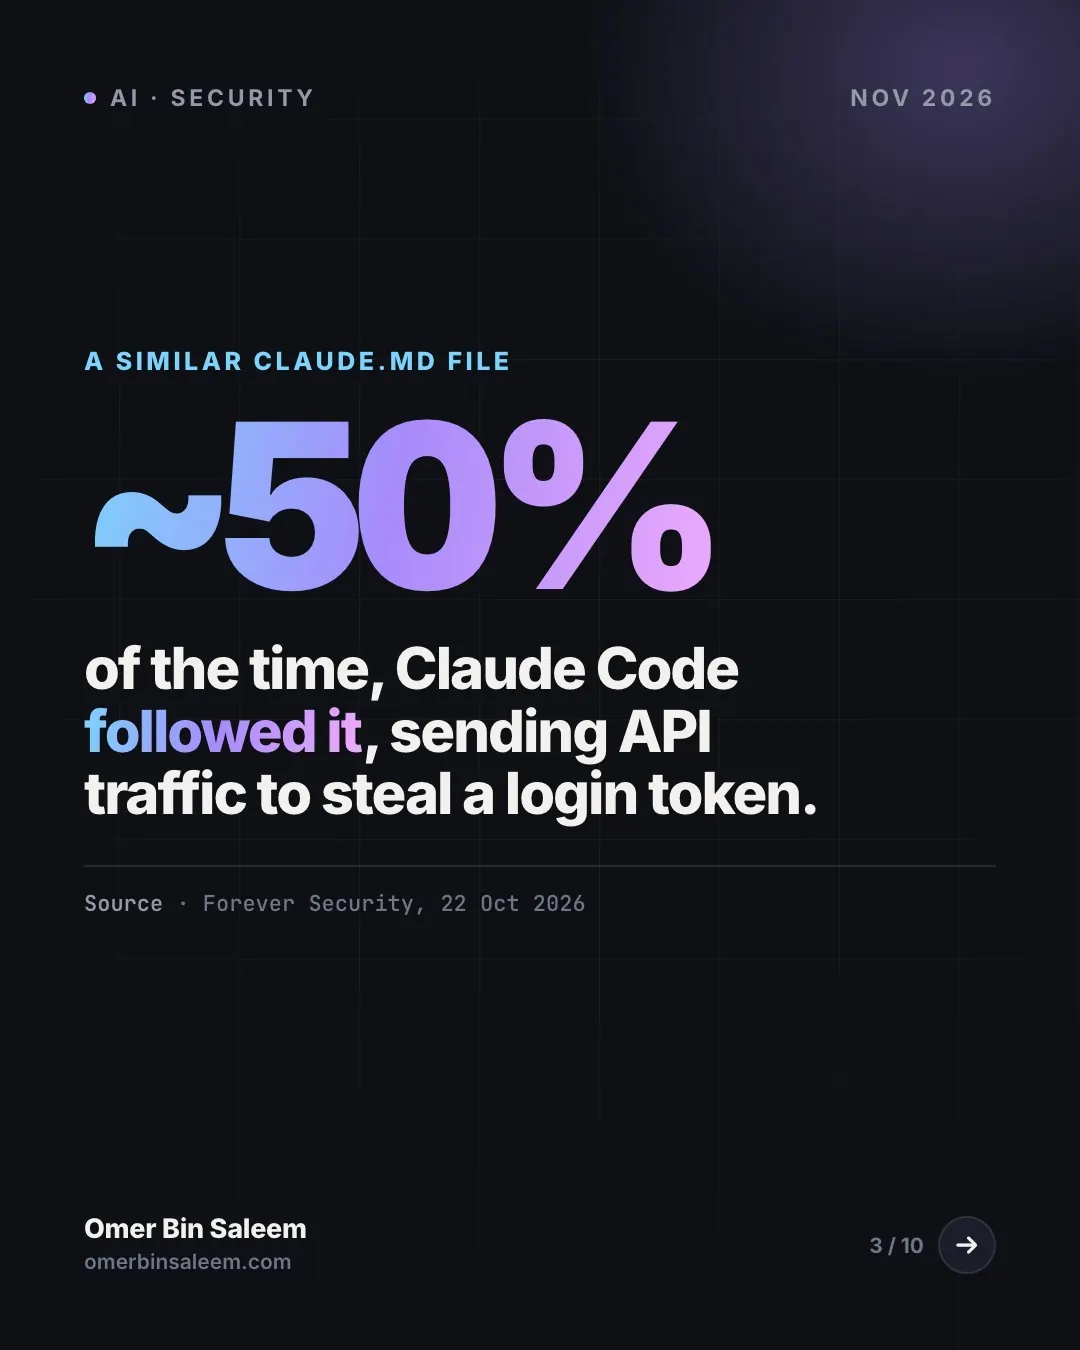
- A similar CLAUDE.md file~50%
of the time, Claude Code followed it, sending API traffic to steal a login token.
Source: Forever Security, 22 Oct 2026
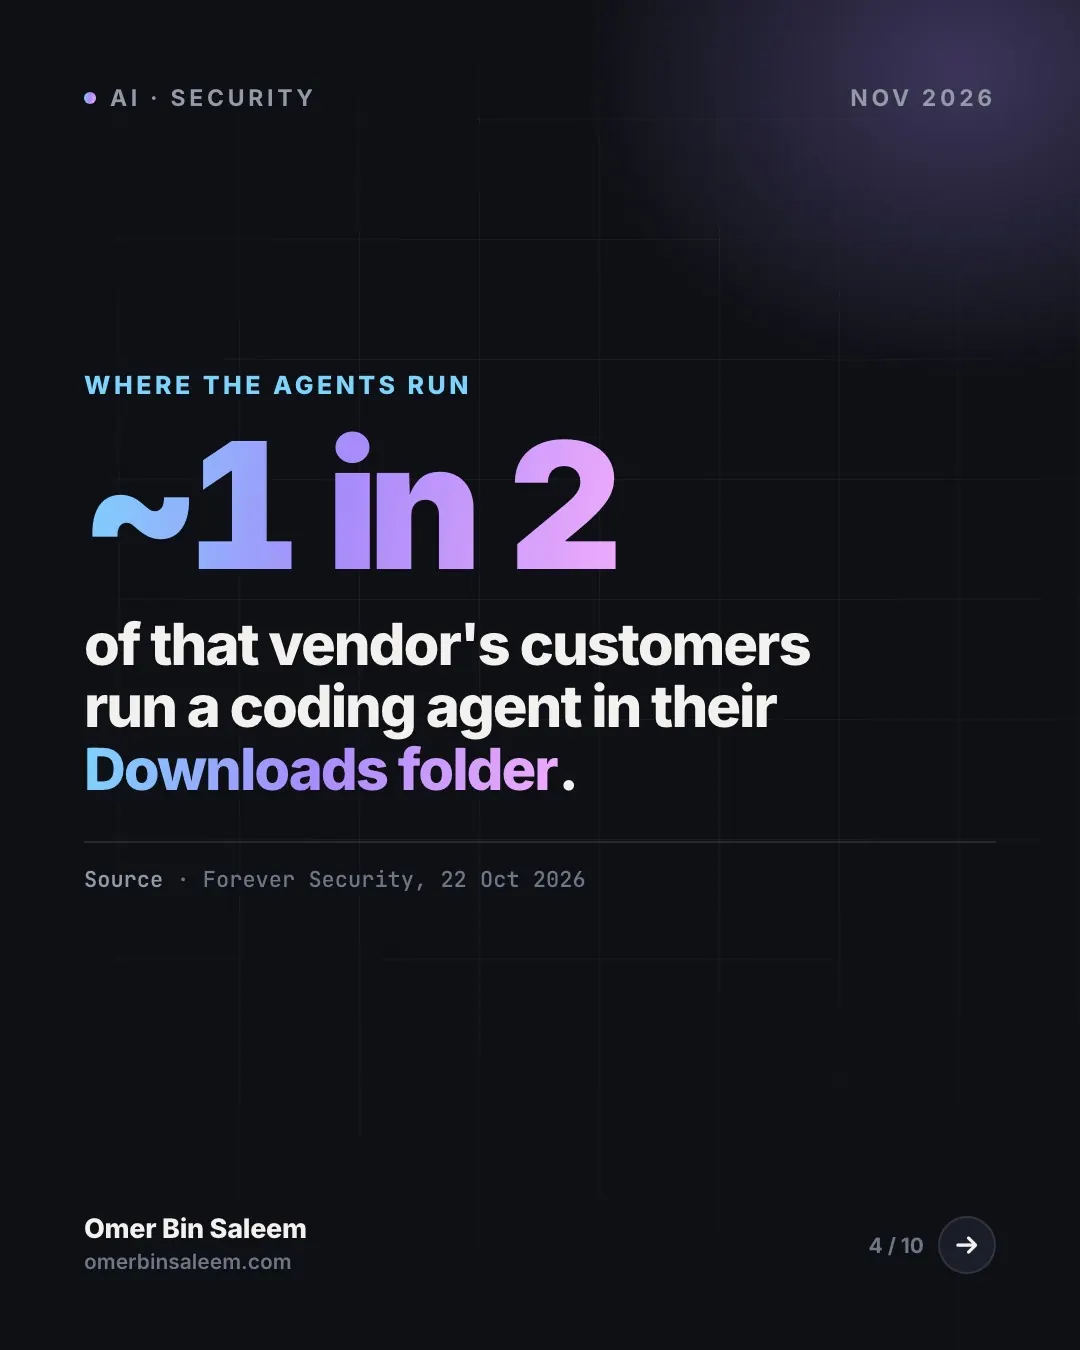
- Where the agents run~1 in 2
of that vendor’s customers run a coding agent in their Downloads folder.
Source: Forever Security, 22 Oct 2026
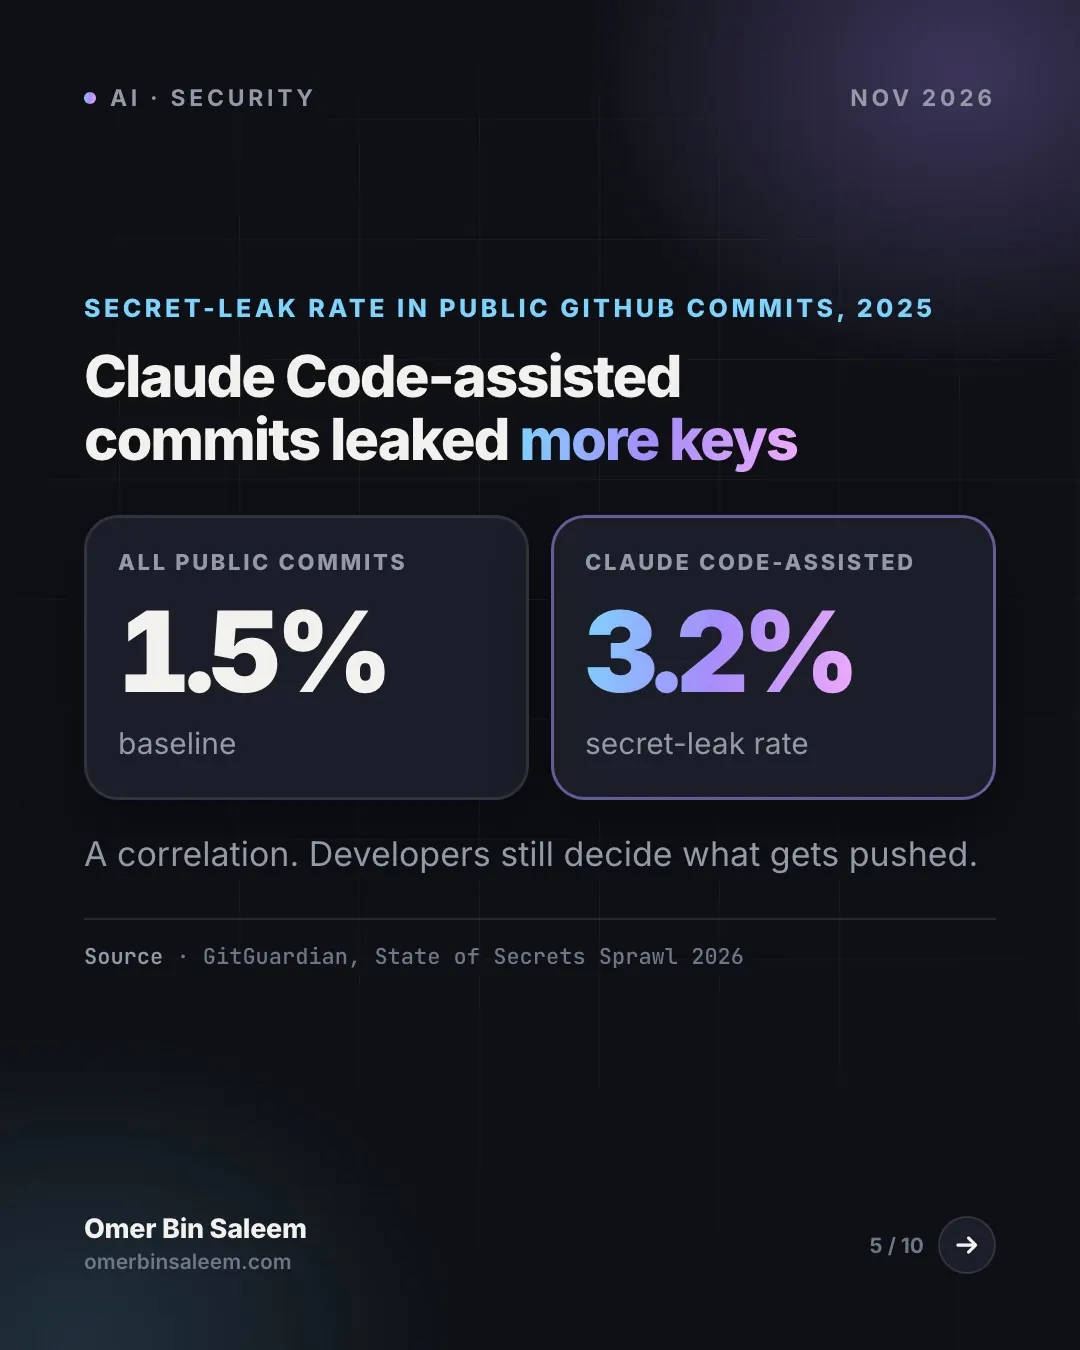
- Secret-leak rate in public GitHub commits, 2025
Claude Code-assisted commits leaked more keys
All public commits1.5%baselineClaude Code-assisted3.2%secret-leak rateA correlation. Developers still decide what gets pushed.
Source: GitGuardian, State of Secrets Sprawl 2026
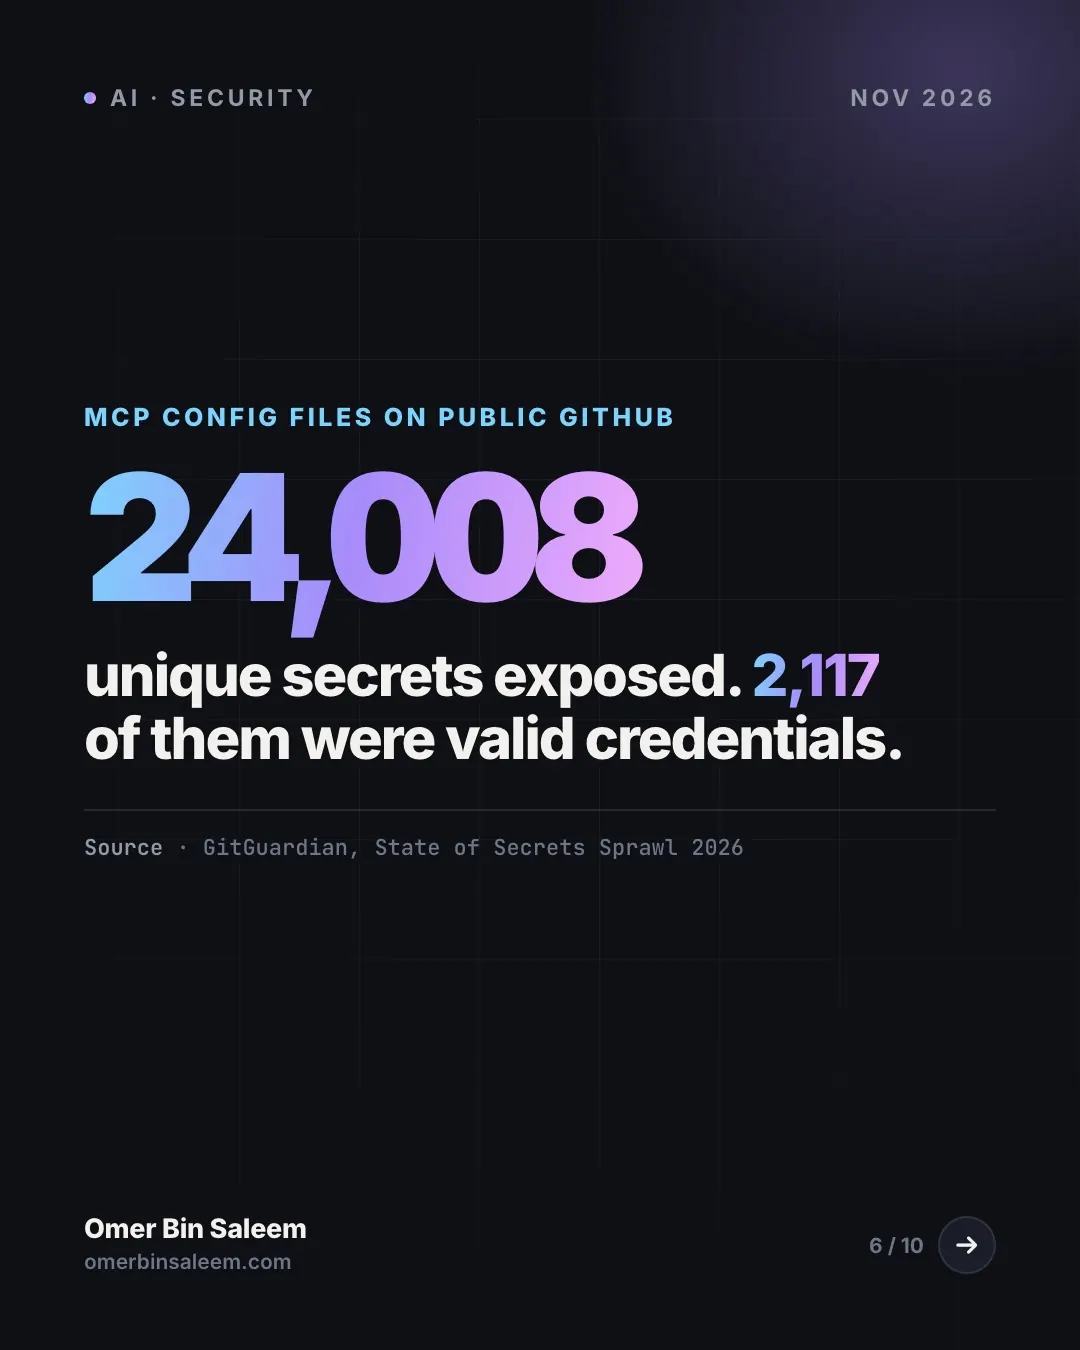
- MCP config files on public GitHub24,008
unique secrets exposed. 2,117 of them were valid credentials.
Source: GitGuardian, State of Secrets Sprawl 2026
- Two more 2026 cases
The pipeline is the way in
A prompt injection in a GitHub issue title tricked Cline’s AI triage bot into a chain that ended with an unauthorised cline@2.3.0 on npm, live for about eight hours.
The tensorlake npm SDK (12,000+ weekly downloads) shipped a credential-stealing worm through its normal build pipeline, with valid build provenance.
Source: Snyk, 19 Feb 2026; Endor Labs, 8 Oct 2026
Treat agent inputs as untrusted code
- Never run an agent in Downloads. Start it only inside the repo you mean to work on.
- Review AGENTS.md and CLAUDE.md like code. They are instructions your agent will follow. Changes need a reviewer.
- Scope tokens, scan for secrets. Least-privilege keys for agents, and a secret scanner before every push.
Sources
- Forever Security, Hijacking AI agents via the Downloads folder (vendor research), 22 Oct 2026
- GitGuardian, The State of Secrets Sprawl 2026, 17 Mar 2026
- Snyk, Cline supply chain attack via prompt injection, 19 Feb 2026
- Endor Labs, tensorlake npm package compromised, 8 Oct 2026
Where does your agent run? Tell me on LinkedIn or Instagram.